Zcash's mainnet launched on October 28, 2016, but the ideas behind it are older than that date suggests, and where they came from explains more about what Zcash actually is than the launch date does on its own.
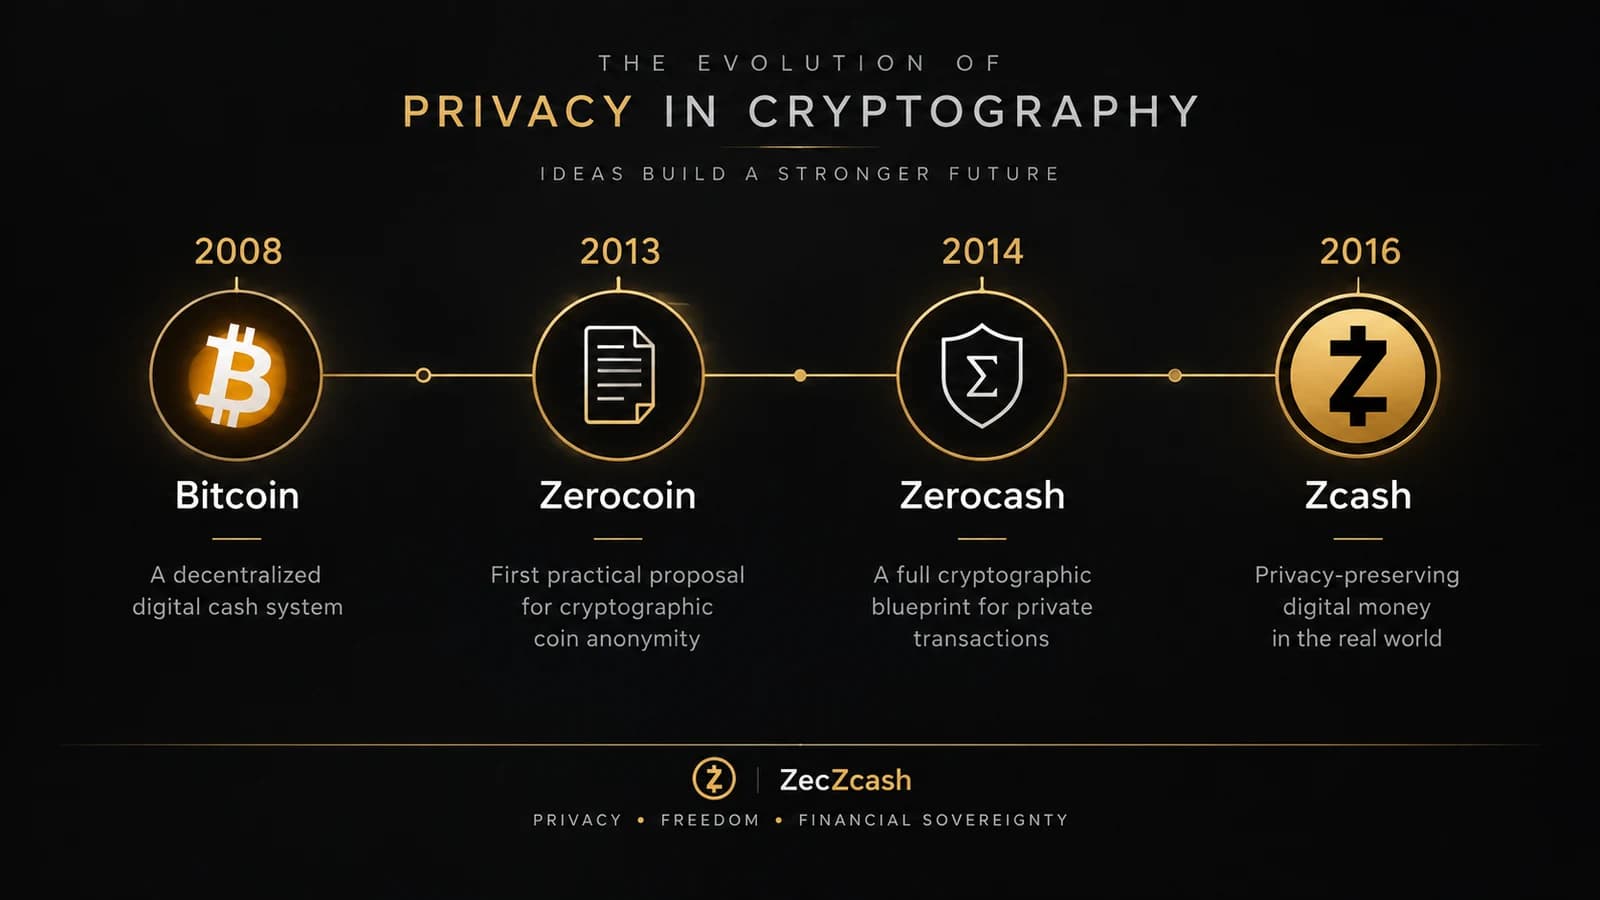
Bitcoin, in 2008, solved a problem that had defeated earlier attempts at digital cash: how a decentralized network agrees on who owns what without a central authority keeping the books. Its solution was a public ledger — every transaction, permanently visible to anyone who looks. Satoshi Nakamoto's whitepaper addressed privacy directly, in a section devoted to it, and proposed pseudonymity as the mitigation: transact through public keys not directly tied to a real identity, and generate a new key pair for every transaction to limit what any observer could link together. The whitepaper was also explicit about that approach's limit — once a single transaction reveals an owner's identity, everything else connected to it in the transaction graph is exposed too.
Closing the gap between "pseudonymous" and "actually private" became the project of a separate line of academic cryptography, starting five years later — not a continuation of Bitcoin's own design, and not something Nakamoto's whitepaper anticipated or endorsed.
2013 — Zerocoin, a privacy patch for Bitcoin
In 2013, Johns Hopkins researchers Ian Miers, Christina Garman, Matthew Green and Aviel Rubin published "Zerocoin: Anonymous Distributed E-Cash from Bitcoin" at the IEEE Symposium on Security and Privacy. Zerocoin was not an early version of Zcash — it was proposed as an extension bolted onto Bitcoin itself, not its own currency.
The problem it targeted was specific: Bitcoin addresses may be pseudonymous, but the transaction graph connecting them is entirely public, and once one address is tied to a real identity, blockchain analysis can trace outward from it. Zerocoin let a user convert bitcoins into "zerocoins" and back, breaking that specific link — a spender could prove their coin belonged to a valid, already-minted set without revealing which one. It didn't hide amounts or a transaction's full origin and destination; it hid which specific coin, out of the set, was being spent. That was a real result, but it fell short of what its authors wanted next: a currency where amounts, senders and recipients could all stay private by default, not just unlinkable within a set.
2014 — Zerocash and the zk-SNARK breakthrough
A year later, largely the same research group — Eli Ben-Sasson, Alessandro Chiesa, Christina Garman, Matthew Green, Ian Miers, Eran Tromer and Madars Virza — published "Zerocash: Decentralized Anonymous Payments from Bitcoin." Zerocash used zk-SNARKs (zero-knowledge succinct non-interactive arguments of knowledge), a proof system that lets one party convince another that a statement is true without revealing why it's true, in a proof that's small and fast to check.
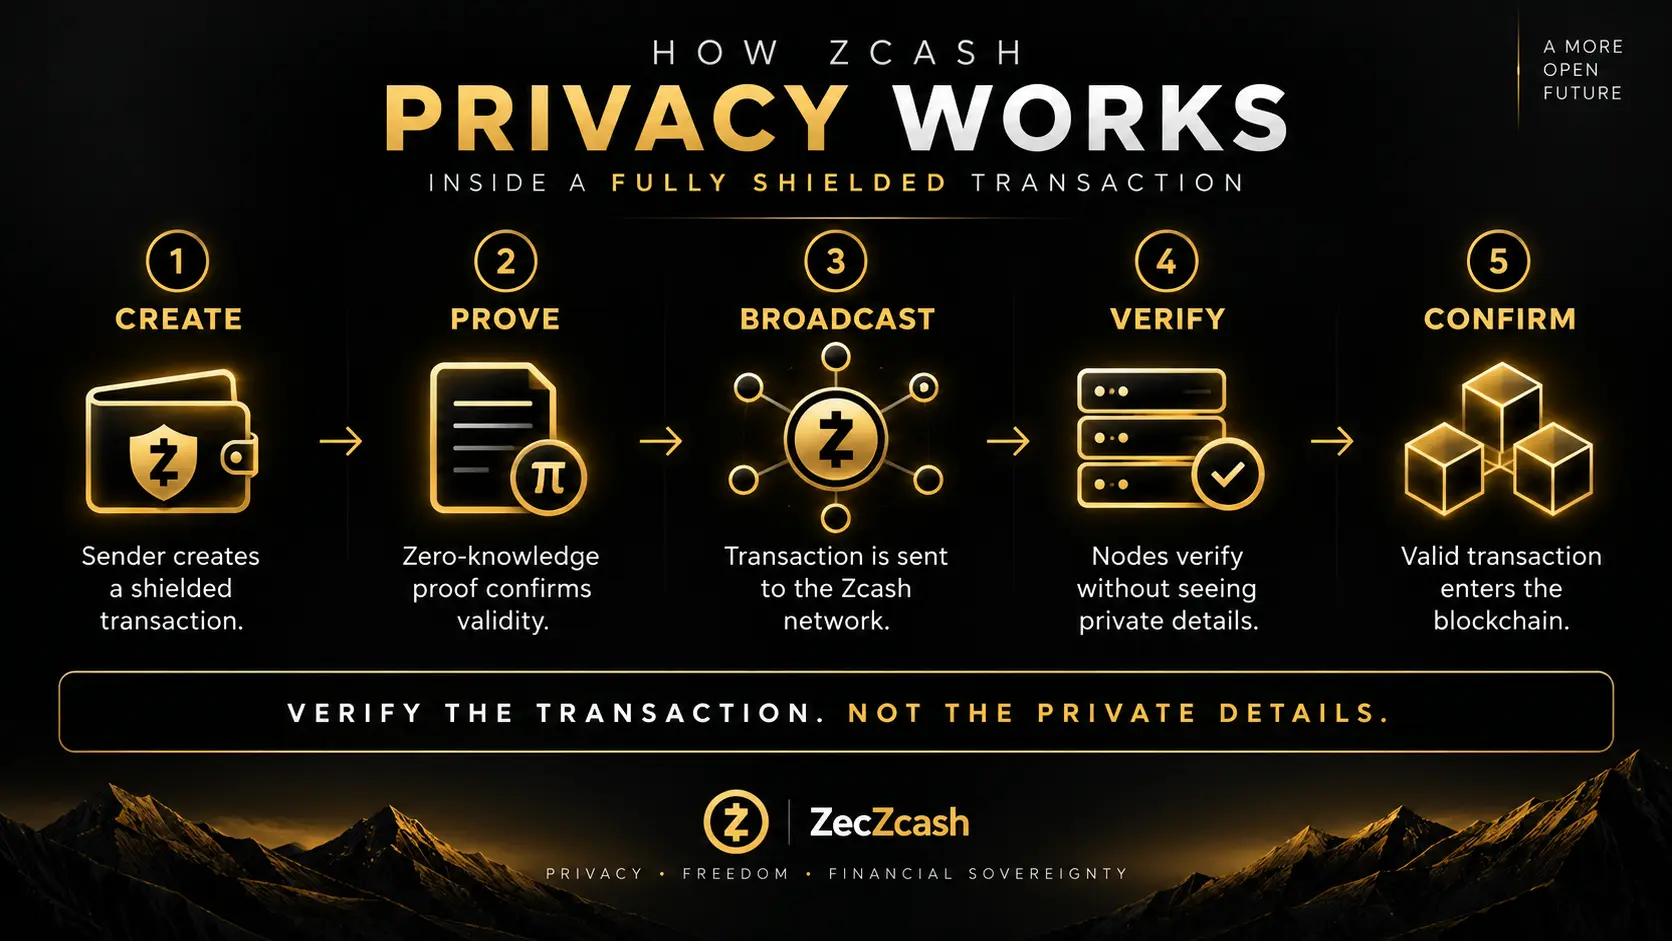
Applied to payments, this changed what was achievable. Rather than proving a spent coin belonged to some valid set, a Zerocash transaction could prove an entire set of rules had been followed — the sender had the funds, nothing was double-spent, no money was created from nothing — without revealing the sender, recipient, or amount to anyone verifying it. That's the specific capability that became Zcash's shielded pool — worth stating precisely, since Zcash later shipped with both shielded and transparent address types, and a transaction touching a transparent address still reveals what a Bitcoin one would. See What Is Zcash? for how that choice works for a user today.
2015–2016 — From paper to protocol
A research paper is not a currency. Turning Zerocash into a running network required software, a consensus mechanism, an economic policy, and a set of cryptographic parameters the zk-SNARK proving system depended on.
The company that built it was legally registered as Zerocoin Electric Coin Company, LLC in 2015 — a legal name it kept; its public branding changed instead, operating as "The Zcash Company" before announcing, on February 21, 2019, that it would go by "Electric Coin Company," partly to avoid confusion with the separate Zcash Foundation. Zooko Wilcox led the effort, and several of the Zerocash paper's own authors, including Garman, joined as founding scientists — closer to the original research team building its own implementation than to an outside company licensing academic work.
Before launch, the team faced a problem specific to the zk-SNARK construction Zerocash used: generating its public parameters required, at some point, the existence of secret information that then had to be destroyed.
October 2016 — The Ceremony
The proving system Zcash launched with — later named Sprout — required what's known as a trusted setup. Generating its parameters meant briefly creating secret values, nicknamed "toxic waste," as a byproduct of the math. If that material survived and fell into the wrong hands, the risk wasn't exposure of anyone's private transaction data — it was counterfeiting. Someone holding it could construct proofs for shielded transactions spending coins that didn't exist, undetectably, because the entire point of the proof system is that a valid proof and an invalid one look identical to a verifier who trusts the parameters.
Zcash's answer was not to trust one party. Parameter generation was split across six independent participants in a multi-party computation, run on October 22 and 23, 2016, each destroying their own secret share after contributing. The security property is easy to state without the cryptography behind it: the parameters stay safe as long as at least one of the six was honest and actually destroyed their share, since reconstructing the toxic waste requires every share.
One of the six worked under a pseudonym: John Dobbertin. Who that was stayed unknown for almost six years.
October 28, 2016 — Zcash launches with Sprout
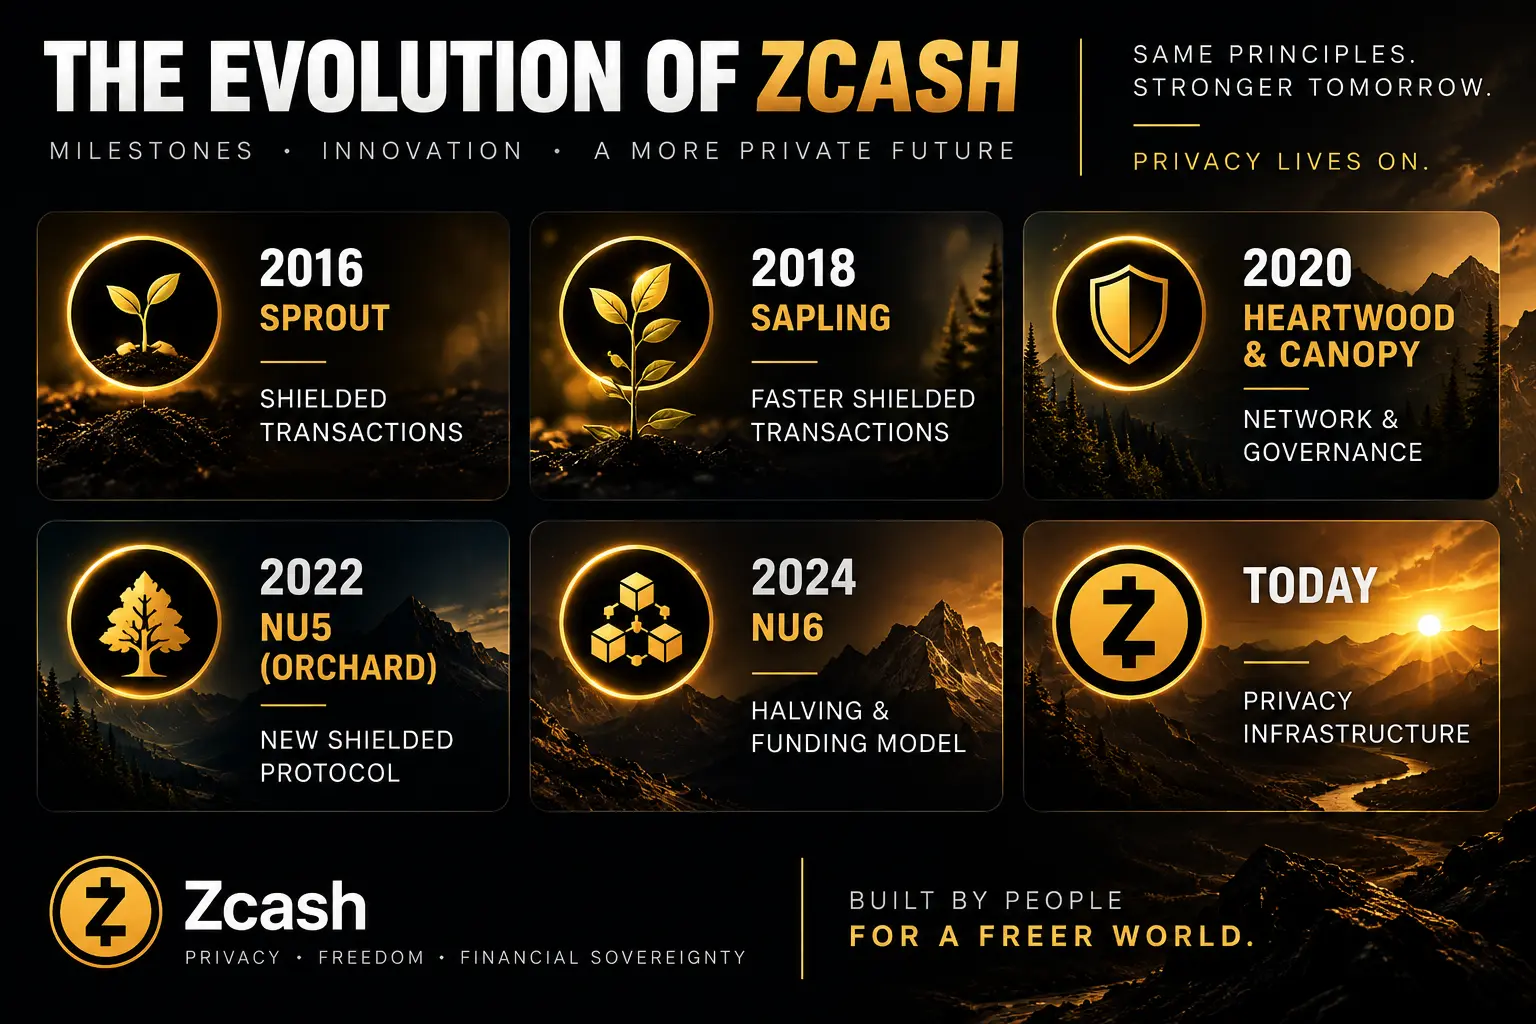
Zcash's mainnet went live on October 28, 2016, days after the Ceremony concluded, with Sprout as its first shielded protocol — the Zerocoin-to-Zerocash line of research running on a live, adversarial network for the first time, rather than in an academic prototype. It also showed the cost of that first generation clearly: constructing a single shielded transaction took tens of seconds and required gigabytes of memory, workable on a desktop but impractical on a phone. Shielded Zcash existed, but using it routinely didn't yet make sense on most people's devices — a gap, along with the trusted setup the system still depended on, that defined the protocol's next several years.
2017 — An independent Zcash Foundation
In 2017, the Zcash Foundation was incorporated as an independent nonprofit, distinct from the for-profit Electric Coin Company, to steward the protocol and support privacy-preserving cryptography as a public good. Zcash had launched with one company doing nearly all its engineering; a year later, protocol direction had at least two organizations with a stake in it.
October 2018 — Sapling
Sapling activated on October 28, 2018, at block height 419,200, replacing Sprout's proving system with a faster one and a redesigned circuit. Per Electric Coin Company's own published figures, it cut the time to construct a shielded transaction by about 90% and memory requirements by more than 97% — minutes down to seconds, on ordinary hardware. That's what made shielded Zcash usable in a mobile wallet, rather than something that existed mostly in theory. Sapling also removed a flaw in Sprout's proving system that was disclosed only in 2019; see has Zcash ever been counterfeited?.
Sapling's own parameters still needed a setup ceremony, but the process had changed: rather than six participants, it drew on a far larger, publicly documented multi-party computation, spreading the same trust assumption across many more contributors than Sprout's had. That made the ceremony safer. It didn't eliminate it — that was still a separate, unsolved problem.
Alongside Sapling, Zcash activated Overwinter, Blossom, Heartwood and Canopy over the next two years: groundwork for future upgrades, a block-time adjustment, coinbase shielding and light-client support, and Zcash's first halving paired with a new development-fund structure. None touched the shielded proving system directly, but together they established that Zcash would keep changing its own consensus rules on a schedule — a mechanism the upgrades that mattered cryptographically would later depend on. For exact dates and block heights, see Zcash Network Upgrades: A Complete Timeline; this account is about why that upgrade path existed, not a rerun of its schedule. Through every one of these changes, Proof-of-Work mining — largely unchanged in its own basic mechanics since 2016 — is what actually confirmed each new block; see How Zcash Mining Works for how that process works today.
2019 — Halo removes the ceremony
In 2019, Electric Coin Company cryptographers Sean Bowe, Jack Grigg and Daira Hopwood published Halo, describing a way to compose zero-knowledge proofs recursively — using one proof to verify another — without the kind of trusted setup Sprout and Sapling both needed. The 2016 Ceremony had tried to make a trusted setup survivable by splitting it across six people; Sapling's ceremony tried to make it safer still by splitting it across many more. Halo asked a different question: could the proving system's reference parameters come from public randomness instead of secret material in the first place, leaving nothing that needed to be destroyed and no toxic waste to worry about at all.
That's a different kind of fix than a bigger ceremony — it doesn't distribute trust more widely, it removes the category of risk the Ceremony existed to manage. The idea took three more years to reach a live Zcash shielded pool.
May 2022 — NU5, Orchard, and a name finally revealed
NU5 activated on May 31, 2022, at block height 1,687,104, introducing Orchard — a new shielded pool built on Halo 2, an evolution of Bowe's earlier work — alongside Unified Addresses, bundling transparent and shielded receivers into one address format. Orchard needed no trusted setup at all. (For how the proving system works under the hood, see How Zcash Works.) You can look up that activation block yourself in the Zcash Explorer.
Set beside 2016, the contrast is direct: six people once ran an elaborate, carefully audited procedure because the cryptography required secret material that had to be perfectly destroyed. Six years later, Zcash's newest shielded pool used a proving system engineered so that requirement didn't exist.
The same year closed a different loop. On April 27, 2022, Zcash Media — an independent educational outlet, not Electric Coin Company or the Zcash Foundation — published a video in which Edward Snowden confirmed, in his own words and with his own cooperation, that he had been John Dobbertin. Snowden had taken part in the 2016 Ceremony as one of its six independent participants; he was never a Zcash founder or developer, and his role began and ended there. For nearly six years, only he and a small number of people around him had known.
2026 — The Orchard vulnerability
Orchard ran without incident for four years. In April 2026, Shielded Labs — an independent Zcash protocol-engineering nonprofit — engaged security researcher Taylor Hornby specifically to look for this kind of flaw. On May 29, 2026, using a custom AI-assisted audit framework built on Claude Opus 4.8, pointed at the Halo 2 and Orchard circuit implementation, Hornby found a critical soundness flaw: a missing constraint that let a prover construct a proof which looked valid without actually satisfying the rule it was supposed to enforce. With the model's assistance, he wrote a complete working exploit and, rather than testing it against the live network, disclosed it immediately to Zcash Open Development Lab — the group that had taken over Zcash's core engineering after 2026's earlier reorganization (more below) — which coordinated an emergency response.
A soft fork at block 3,363,426, around 02:00 UTC on June 2, disabled new Orchard transactions entirely; the NU6.2 hard fork, at block 3,364,600 roughly a day later, shipped a corrected circuit and restored Orchard.
Exploitation is worth stating precisely rather than reassuringly. Shielded Labs has said it believes prior exploitation is unlikely, based on its own analysis and review by multiple independent researchers, and that the current ZEC supply is sound — a judgment, not a proof. Because Orchard's own privacy properties are what the pool exists to provide, no one can point to a transaction history and rule exploitation out with certainty; that residual uncertainty, which the fix alone couldn't close, is what the next upgrade was built to address.
July 2026 — Ironwood (NU6.3)
NU6.3 (Ironwood) has been active on Zcash mainnet since block 3,428,143 on July 28, 2026. New shielded activity uses the Ironwood pool; Orchard remains spendable but exit-only. Its governing ZIPs (258, 318 and 326) are still listed as Draft in the official zcash/zips index — a document status, not a sign the upgrade is inactive; see the Zcash Network Upgrade Tracker for the sources behind both. Ironwood is not a patch to Orchard but a new shielded pool built on a corrected version of the same design, restricting Orchard to withdrawals only — no new deposits, no internal transfers — while existing value moves out of Orchard across the turnstile into Ironwood, at each holder's own pace, keeping the migration observable at the pool boundary.
Ironwood also came with a formal-verification effort distinct from the code fix itself: a machine-checked proof, written in the Lean proof assistant, comprising more than 2,700 individually verified theorems. Its scope matters — the proof establishes a specific property called balance integrity, that Ironwood's shielded pool cannot pay out more value than has verifiably entered it, covering the proof system, circuit rules and ledger accounting relevant to that property. It is not a claim that the entire protocol has been formally verified; it's a machine-checked argument about the one property a repeat of the Orchard bug would have violated.
That's a third distinct way Zcash has handled the same underlying question — how to trust the math without trusting a person. The Ceremony split trust among six people. Halo tried to remove the need for secret trust altogether. Ironwood's proof adds something different again: machine-checked reasoning about the specific property that mattered most, produced after a real failure showed what could go wrong when it wasn't checked this way to begin with.
An institution rebuilt too
The Orchard incident connects to Zcash's institutional history in a specific way worth noting briefly. In January 2026, Electric Coin Company's entire engineering team left after a dispute with Bootstrap, the nonprofit board overseeing it, and founded Zcash Open Development Lab — the same organization Hornby disclosed the Orchard flaw to four months later. ZODL raised over $25 million in seed funding and took over development of what had been ECC's Zashi wallet, rebranded to Zodl.
One detail closes a longer loop: among the Bootstrap board members whose disagreement with ECC's team preceded the split is Christina Garman, co-author of both the 2013 Zerocoin and 2014 Zerocash papers and a Zcash co-founder — the same person who helped originate the cryptography was still, thirteen years later, part of the structure deciding Zcash's direction. For the fuller account, see Who Runs Zcash?
What comes next: NU7
As of this writing, Zcash's next upgrade has not activated. NU7, under ZIP 218, would cut target block time from 75 to 25 seconds without changing the underlying issuance schedule, alongside retiring version 4 transactions and changes to the development-funding mechanism. In a September 2026 coinholder vote — about 2.4 million of 3.6 million eligible ZEC participating — 99.9% of votes backed the block-time change specifically. NU7 has been active on testnet since October 4, 2026 (block 4,465,026); a final go/no-go decision for mainnet is expected around October 20, ahead of a tentative November 5 mainnet target. None of those dates are guarantees — NU7 becomes part of this history once it actually activates, not before. For the current, continuously verified status of NU7 and every other Zcash network upgrade, see the Zcash Network Upgrade Tracker.
Zcash history at a glance
- 2008 — Bitcoin's whitepaper describes a public ledger and the limits of pseudonymity
- 2013 — Zerocoin proposes breaking the coin-to-history link on Bitcoin
- 2014 — Zerocash uses zk-SNARKs to hide sender, recipient and amount
- 2015 — Zerocoin Electric Coin Company founded to build the protocol
- Oct 2016 — The Ceremony (Oct 22–23); Zcash launches with Sprout (Oct 28)
- 2017 — Zcash Foundation incorporated as an independent nonprofit
- Oct 2018 — Sapling makes shielded transactions practical on phones
- 2019 — Halo removes the need for a trusted setup
- May 2022 — NU5 activates Orchard and Halo 2; Snowden confirmed as Dobbertin
- May–Jun 2026 — Orchard soundness bug found and fixed via NU6.2
- Jul 2026 — NU6.3 activates Ironwood at block 3,428,143, with a formally verified balance-integrity proof (governing ZIPs still listed as Draft)
- Pending — NU7, targeting faster blocks, not yet activated
What this history actually shows
Zcash gets described, often, as simply a "privacy coin" — a label that flattens a more specific story. Several foundational parts of its shielded architecture have been replaced or redesigned over time: the proving system itself, four times over so far (Sprout to Sapling to Orchard to Ironwood); the trust it depended on, from a six-person ceremony to a wider one to a system engineered to need no ceremony at all; and, this year, the standard for what counts as assurance, from checked code to a machine-checked proof of the one property that had actually failed.
None of that happened because the earlier versions failed in any simple sense — Sprout worked, Sapling worked, Orchard worked for four years before its flaw was found. Each version exposed, precisely, what the next one needed to fix. That's worth understanding if the goal is to know what Zcash actually is, not just when it launched.
This page is updated as major events happen. If you spot something outdated, let us know in the @ZecZcash Telegram channel.